

80% of ANZ firms hit by cyberattacks, Claroty says
Thu, 8th Oct 2026 (Today)
Claroty says 80% of organisations in Australia and New Zealand experienced a cyberattack on their operational environments in the past year, with average financial losses of USD $2.04 million.
The findings come from a survey of 2,000 business and technology leaders across more than 40 countries and indicate a higher cost burden in Australia and New Zealand than the global average of USD $1.04 million.
In the region, respondents said the most significant effects of attacks on operational environments were operational downtime, cited by 41%, followed by safety incidents or hazards at 37% and reputational damage at 32%.
Organisations reported an average of about two hours of operational downtime after their most significant cyber incident. Another 18% said downtime lasted more than three days.
Many incidents were linked to third-party remote access. In Australia and New Zealand, 88% of organisations had faced at least one cyber incident originating from third-party access in the previous 12 months, with an average of more than three such incidents per organisation.
That exposure was accompanied by limited oversight of external connections. More than half of respondents, 52%, said they had only partial or no monitoring of third-party connections into their cyber-physical systems and operational technology environments.
AI risks
The research also examined how organisations are using artificial intelligence in operational settings. Across Australia and New Zealand, 83% said they were already using AI in some form.
While 49% said AI had improved operational efficiency and productivity, and 46% said it had improved decision-making, 45% said it had introduced new cybersecurity and compliance risks.
Asked about the biggest threats facing operational environments, 32% pointed to AI-powered cyberattacks, followed by vulnerable legacy operational technology systems at 30%.
The survey suggests security concerns are becoming more closely tied to broader technology modernisation efforts. Respondents identified strong cyber-physical systems security and risk management as the most important factor in successful digital transformation in the region, at 33%.
Compliance pressure
On compliance, 74% of organisations said they took a proactive or structured approach to cybersecurity compliance in operational environments. Even so, many said practical barriers remained.
The biggest operational obstacle to full compliance was a lack of alignment between IT and OT teams, cited by 31% of respondents. Limited visibility and third-party risk followed at 23% each.
Nearly half, 45%, said keeping pace with changing cybersecurity regulations, standards and frameworks was their biggest compliance challenge. Another 36% said managing compliance across multiple sites or business units was difficult.
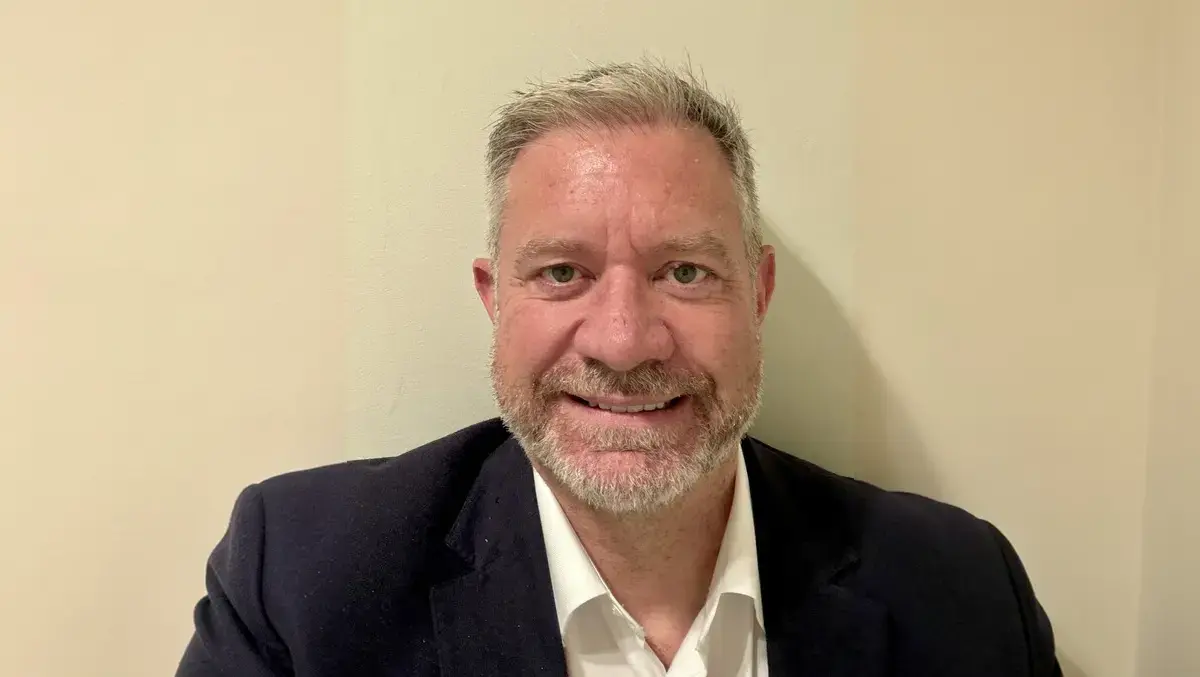
Jason Pearce, Field CTO - APJ at Claroty, said the higher financial impact in the region should change how organisations think about operational security.
"The ANZ findings are particularly significant because local organisations are experiencing an average financial impact that is almost twice the global average. That reinforces why operational resilience needs to be treated as a business priority, not simply a cybersecurity objective. In operational environments, uptime isn't simply a metric - it is directly connected to business continuity, productivity, profitability, customer trust and, in many critical environments, safety. Even a relatively short disruption to physical operations can create significant downstream consequences," Pearce said.
The survey covered environments including cyber-physical systems, operational technology, internet-connected devices, medical devices and building management systems. These systems sit outside traditional office IT networks but are increasingly connected through digital transformation programmes, remote access tools and AI-based software.
That expanding connectivity has widened the number of entry points available to attackers, particularly where suppliers and contractors need remote access. The findings indicate that, for many organisations in Australia and New Zealand, governance and monitoring of those access channels have not kept pace.
Pearce also linked the issue to a broader shift beyond baseline compliance.
"As organisations continue to digitise and connect their operational environments, cybersecurity also needs to move beyond tick-box compliance. When digital systems interact with physical processes, organisations need continuous visibility of their cyber-physical environment, effective governance and control over risk, and the ability to respond to changes before they become operational disruption. Compliance provides an important baseline, but ultimately resilience is measured by whether critical operations can withstand disruption, maintain safety and recover effectively."