
Fujitsu launches cyber defence tool to prioritise risks
Thu, 29th Oct 2026 (Today)
Fujitsu has launched a cyber defence solution designed to help organisations identify and prioritise cyber risks.
The launch comes as Australian authorities report a rise in cyber incidents, and after the Australian Federal Police arrested two men in Western Australia linked to the TeamPCP cyber syndicate.
The new service combines Attack Surface Management and Cyber Threat Intelligence in a single process to identify internet-facing IT assets, assess risk and guide response efforts. It is aimed at organisations that need to decide which vulnerabilities to address first with limited staff and budgets.
According to the Australian Signals Directorate's 2025-26 Annual Cyber Threat Report, the agency responded to more than 1,500 cyber security incidents during the financial year, up 20% from the previous period. Against that backdrop, Fujitsu is positioning the service around what security teams can see from outside their own networks, including systems they may not realise are exposed.
External view
The service continuously scans for internet-accessible assets and vulnerabilities, including systems outside formal asset registers. These can include test sites, cloud assets and systems introduced through links with partners and suppliers.
The threat intelligence component also looks for customer credentials circulating externally. Combined with vulnerability scanning and third-party data, it is intended to help customers detect overlooked assets and weaknesses earlier.
A second element links the findings to internal asset information, such as configuration management databases, to identify responsible teams, the type of information held and the business importance of each system. The aim is to shift remediation decisions away from technical severity scores alone and towards likely business impact.
The service also includes mechanisms to track response activity and show the status of countermeasures over time. That is intended to give management teams and frontline security staff a shared view of cyber risks and mitigation work across the organisation.
Local pressure
In Australia and New Zealand, the offering is aimed at businesses dealing with alert fatigue and growing complexity in cloud and partner-connected environments. Enterprises are managing broader digital estates as systems spread across internal infrastructure, external providers and connected organisations.
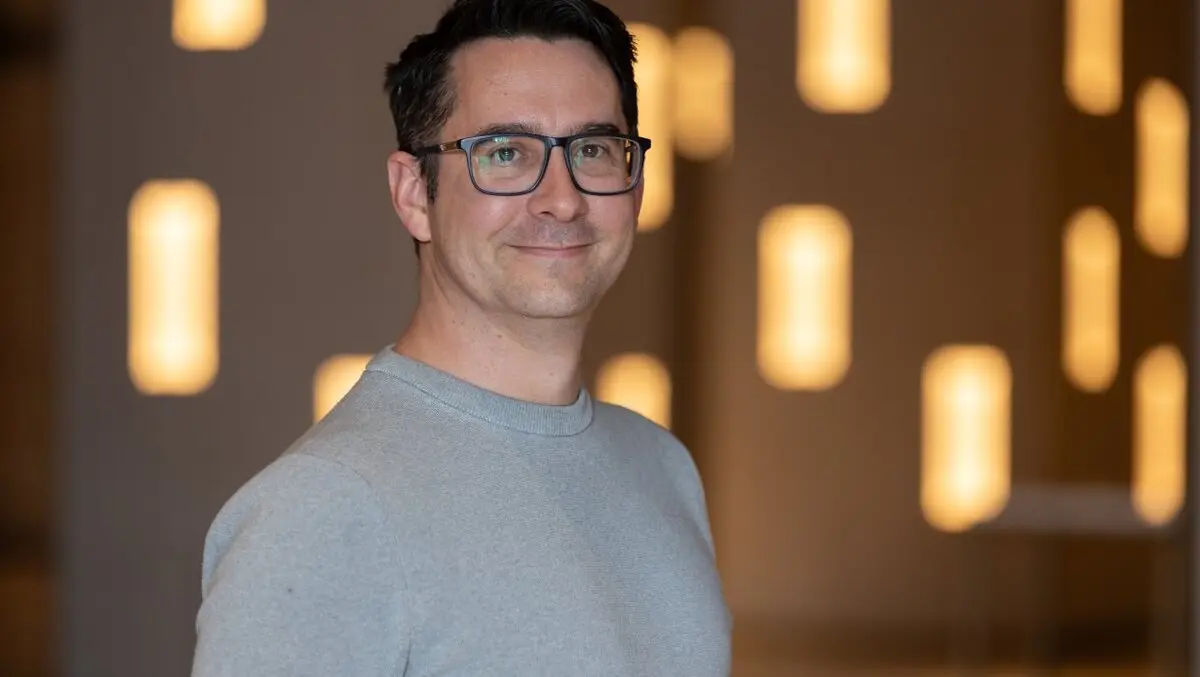
Matt Shaw, Head of Cyber Security and Digital Workplace for Oceania at Fujitsu, said: "Working with customers in key sectors across Australia and New Zealand, we know local security teams are drowning under alert fatigue. The recent TeamPCP bust showed how easily companies get blindsided by software they didn't even know they had. You can't patch what you can't see. Fujitsu's new solution takes the guesswork out of defence. By looking at a network through a hacker's eyes, we filter out the noise and tell teams exactly what to fix first based on actual business risk. That's how we give organisations the confidence to safely innovate and grow."
Fujitsu said the service draws on its broader cyber defence strategy and operational knowledge from its internal security work. The rollout is also tied to its Cyber Security Nerve Centre, which it established earlier this month.
More broadly, internal technology teams are under growing pressure to secure expanding estates without matching increases in headcount. As organisations rely more heavily on cloud services, digital platforms and third-party links, the number of external assets and potential entry points has grown.
That has made asset visibility a central issue for security teams, particularly when dealing with legacy systems, decentralised procurement and development environments set up outside central IT oversight. For many companies, the challenge is not only finding vulnerabilities but deciding which pose the greatest risk to business operations.
Fujitsu said its service is built to support a continuous cycle covering risk identification, assessment, prioritisation, response and verification of whether the response reduced risk.